Find vulnerabilities in your code before they ever reach production
Analyzes code, dependencies, and your live application, with AI and automatic fixes right in your PRs. Install the GitHub App and get started in minutes. Free plan available.

Companies that trust Defender360
Used by regulated businesses across Brazil.
Why Defender360 Security Scan AI
Code security that understands how devs work, zero friction, AI from start to finish.
Automatic fixes delivered via Pull Request
When we find a vulnerability, we open a PR with the fix. You review and accept in minutes, not hours.
A free plan that's actually free
Free forever for solo devs and small projects. Basic static analysis, security badge, and scanning of public GitHub repositories, no credit card required.
Automatic fixes in 9 languages
Python, JavaScript, TypeScript, Go, Java, PHP, Ruby, JSX, TSX. Broad coverage for modern web projects.
From install to automatic fix in under 5 minutes
1. Install the GitHub App
Connect your organization or repository in 2 minutes.
2. Automatic analysis on every PR
Every Pull Request is scanned, code, dependencies, and live application. You get a report right inside the PR.
3. AI suggests the fix
When possible, Scan opens an automatic fix PR, you review and accept.
Everything a secure development team needs
Broad coverage, native GitHub integration, AI from start to finish.
Covers code, dependencies, and live apps
Static, dynamic, and dependency analysis in a single pipeline, nothing extra to install.
Automatic fixes in 9 languages
Python, JavaScript, TypeScript, Go, Java, PHP, Ruby, JSX, and TSX, fixes are delivered via PR.
Real-time security badge
A JavaScript widget that displays your repository's security posture directly in the README.
AI-Assisted Vulnerability Scanning
AI-assisted scanning of your web applications (paid plans).
Dark Web Monitoring
Continuous monitoring of leaked credentials and secrets across multiple breach intelligence sources (paid plans).
Audit-ready reports
Executive report and regulatory assessment with blockchain logging and ICP-Brasil. Ready for LGPD, SOC 2, ISO 27001, and PCI DSS (paid plans).
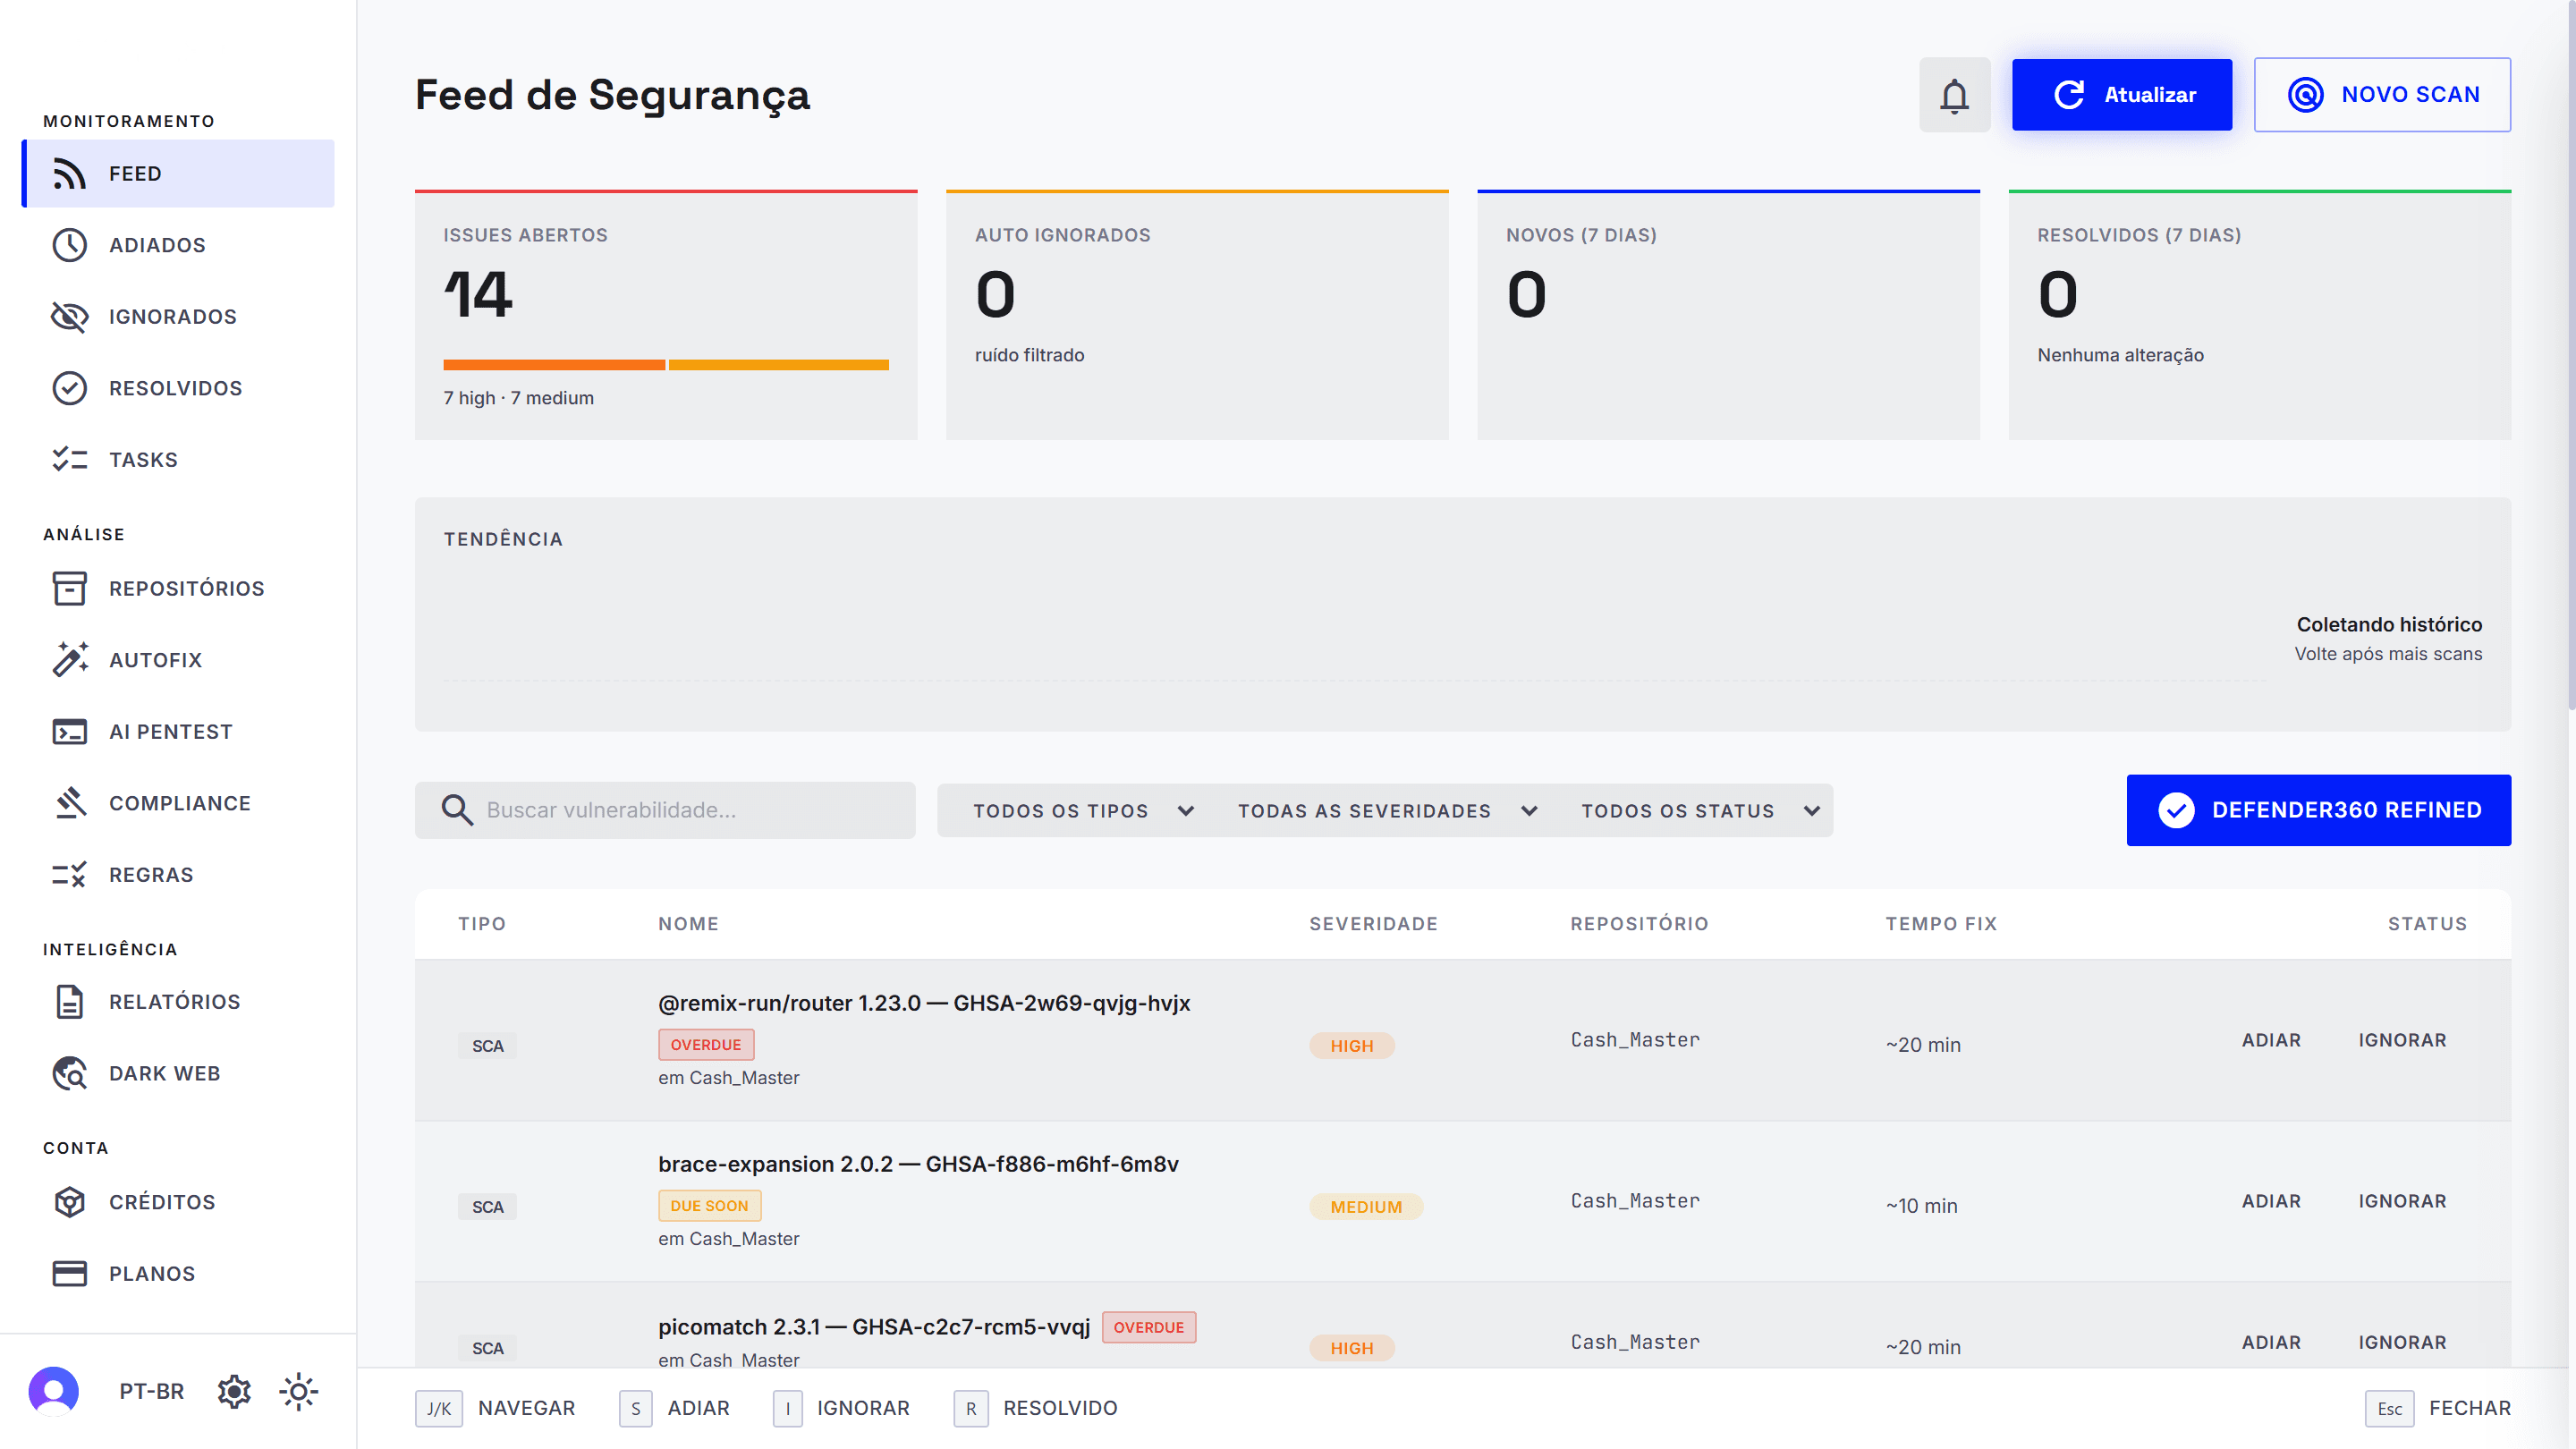
Scan in action
From vulnerability to fix PR, inside your team's workflow.
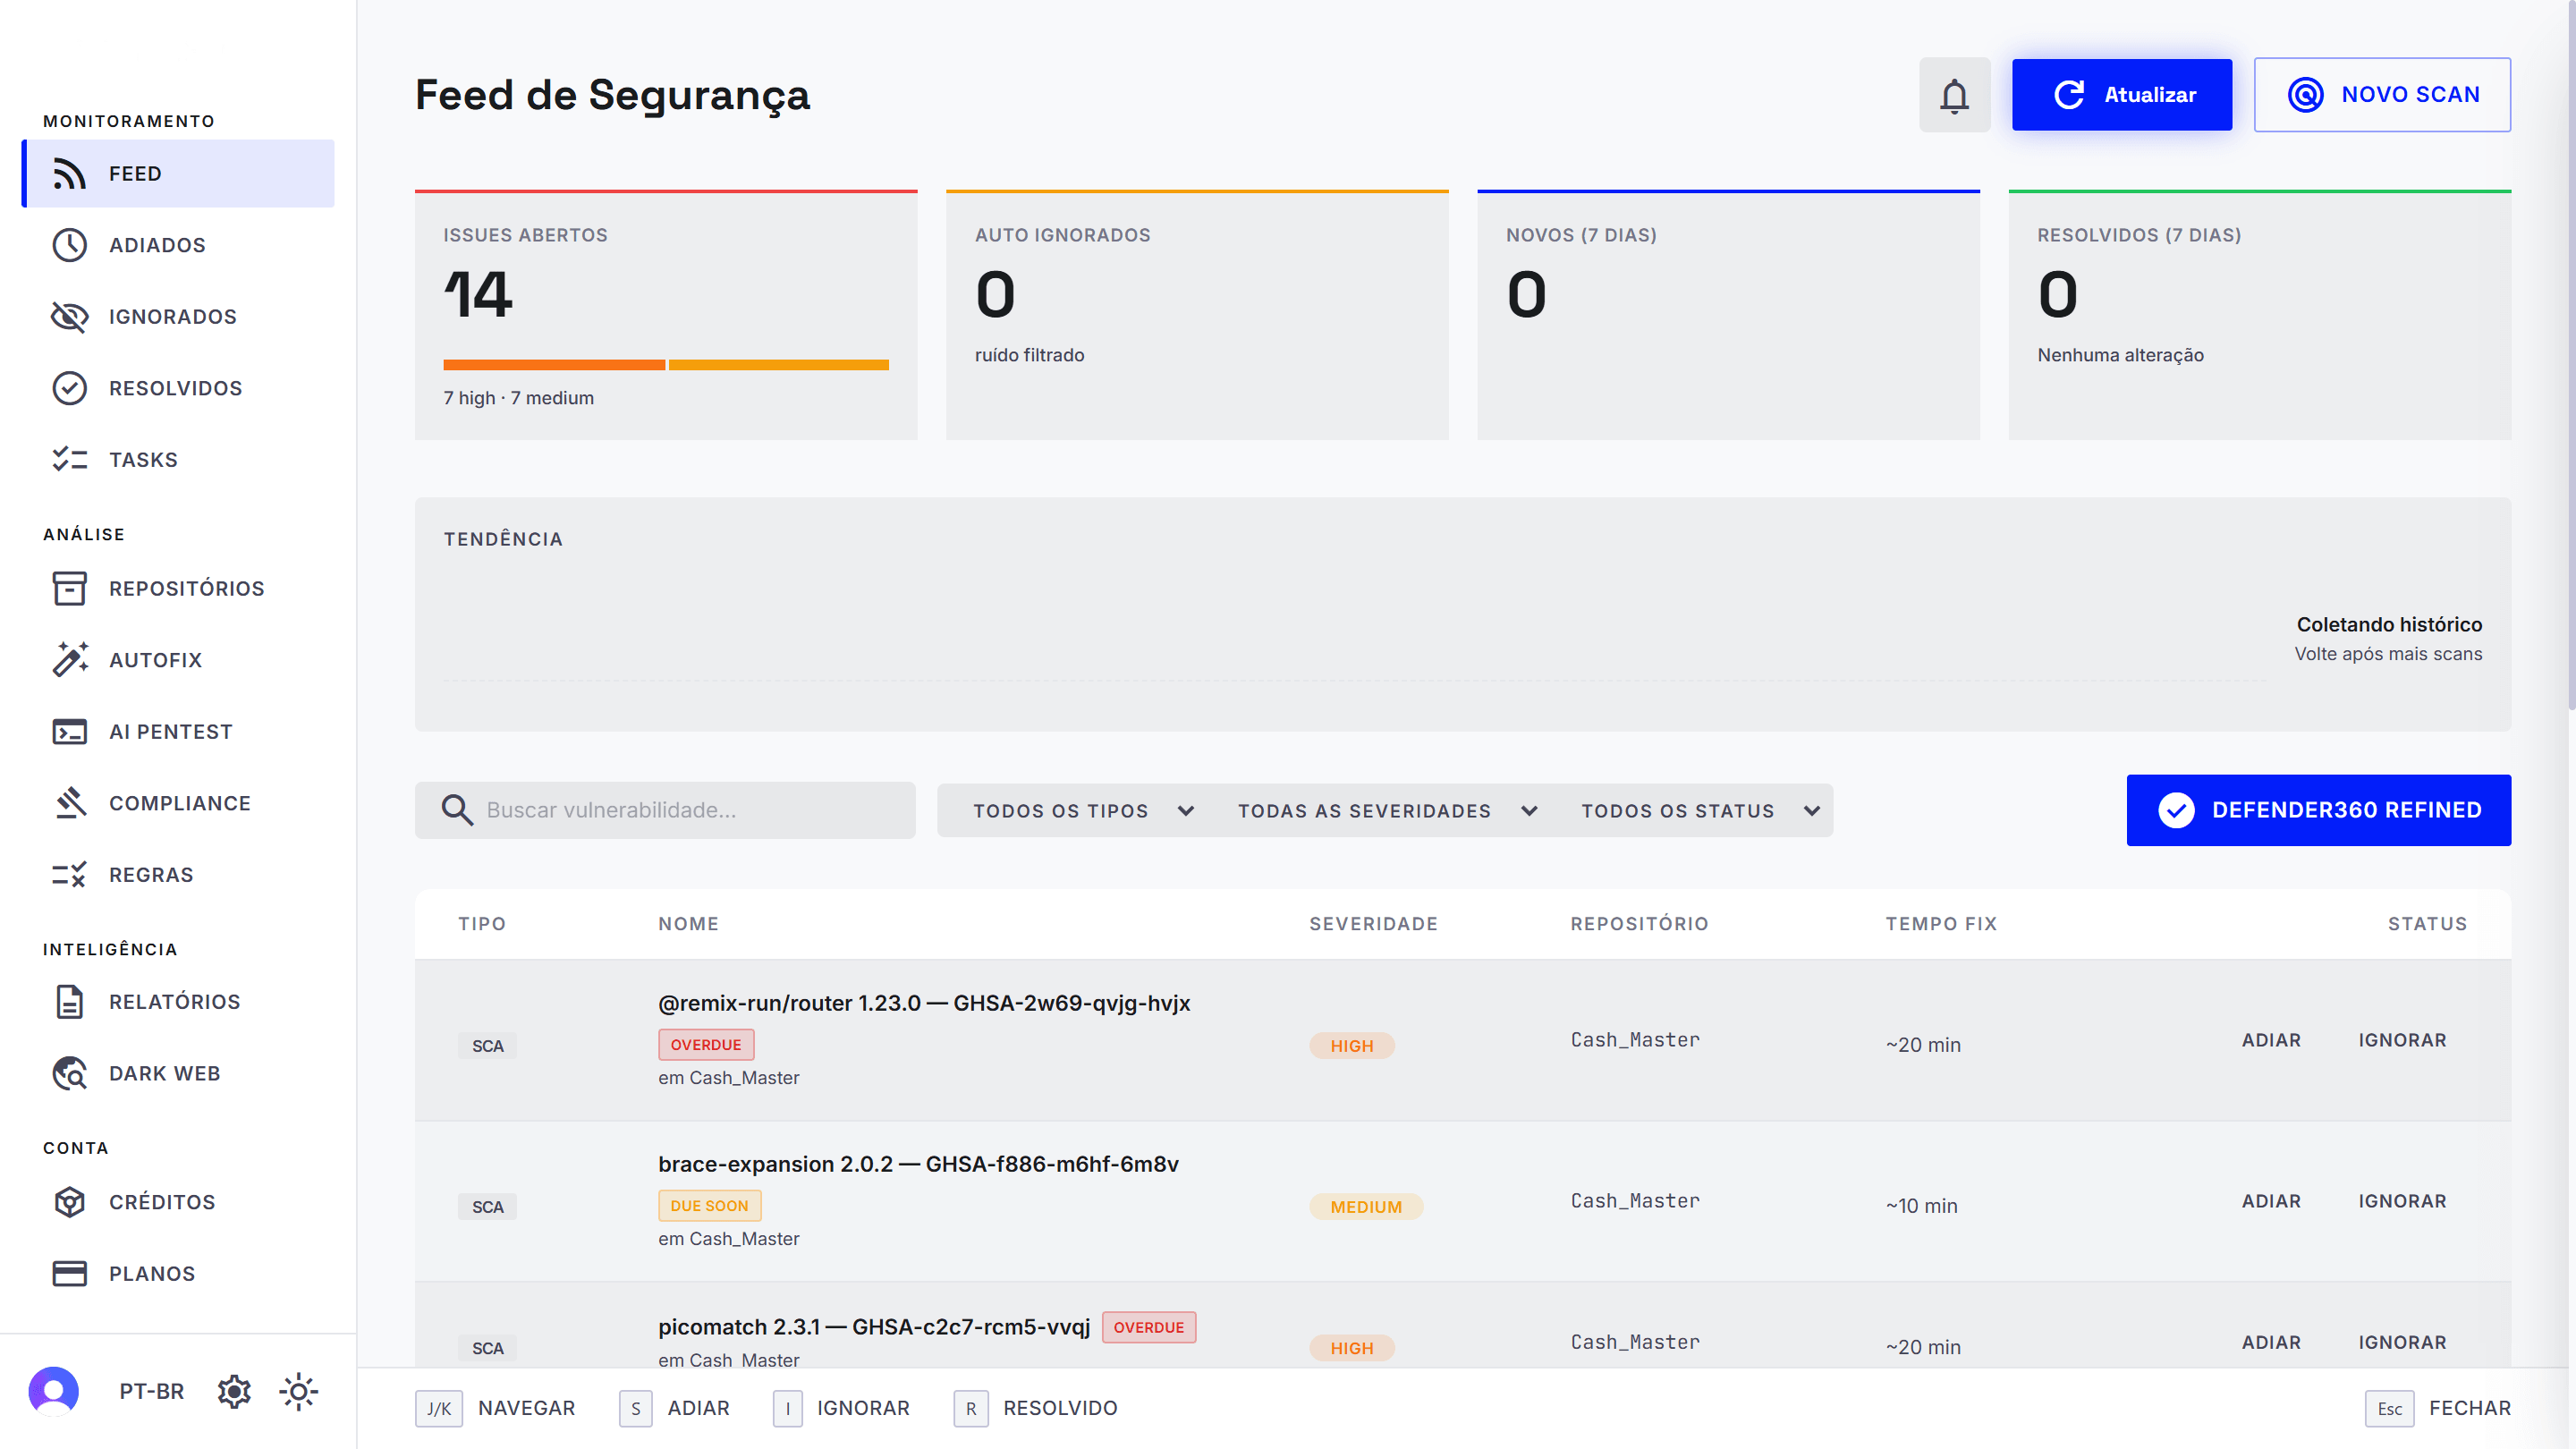


Real screens from Defender360 Security Scan AI.
Automatic fixes in the most widely used production languages
Broad coverage for modern web projects. More languages are on the roadmap.
Languages with automatic fixes
Git platform
GitHub (GitLab and Bitbucket on the roadmap)
Coverage for the frameworks that matter
Automatic vulnerability mapping to the most important frameworks.
Need continuous vulnerability scanning for your entire organization?
Defender360 Security AI is the enterprise security platform with automated BCB 538 reporting, threat intelligence, and dark web monitoring.
Frequently asked questions about Scan
The answers your development team needs before connecting the first repository.
Yes, you can start using Scan for free, connecting your GitHub repository in a few minutes, without waiting for budget approval to try it. The investment in paid plans is far lower than the cost of fixing a vulnerability already in production, and the return shows up in the very first automatically fixed pull requests.
A few minutes: just connect your GitHub organization and Scan starts analyzing the repositories on every push and pull request. There's no need to install agents or train the team before seeing the first results, because the findings appear right in the pull request feed.
Findings appear in the exact context of the pull request, tied to the code being changed, not as a loose, contextless list. On top of that, much of the fixing arrives ready via Autofix, with AI-generated pull requests, so the team reviews and approves instead of investigating and writing the fix from scratch.
Yes, Scan generates compliance reports mapped to frameworks such as OWASP, LGPD, ISO 27001, PCI DSS, SOC 2, and NIST CSF, organizing the technical security evidence for your code. These reports support formal audits and certifications, but they don't replace the audit process itself.
Scan's AI suggests and, with Autofix, opens the fix pull request ready for review in the main languages: Python, JavaScript, TypeScript, Go, Java, PHP, Ruby, JSX, and TSX. Your team stays in control: it reviews, adjusts if needed, and approves the merge. AI removes the repetitive work, not the developer's final decision.
Scan is built for development teams, tech leads, and CTOs who want code security without leaving the GitHub workflow: it connects to the whole organization and analyzes every push and pull request automatically. It also brings AI pentesting to spot risks beyond the source code, on the same platform the team already uses every day.
Get started in 2 minutes. Free forever.
Install the GitHub App and watch vulnerabilities surface right inside your PRs. No credit card required.